Boston Scientific's cyber incident turns a security failure into a guidance problem
The medtech group says the August attack will likely hit third quarter and full year results, and that its July guidance is now unlikely to be met. Investors must wait until October 28 for numbers.
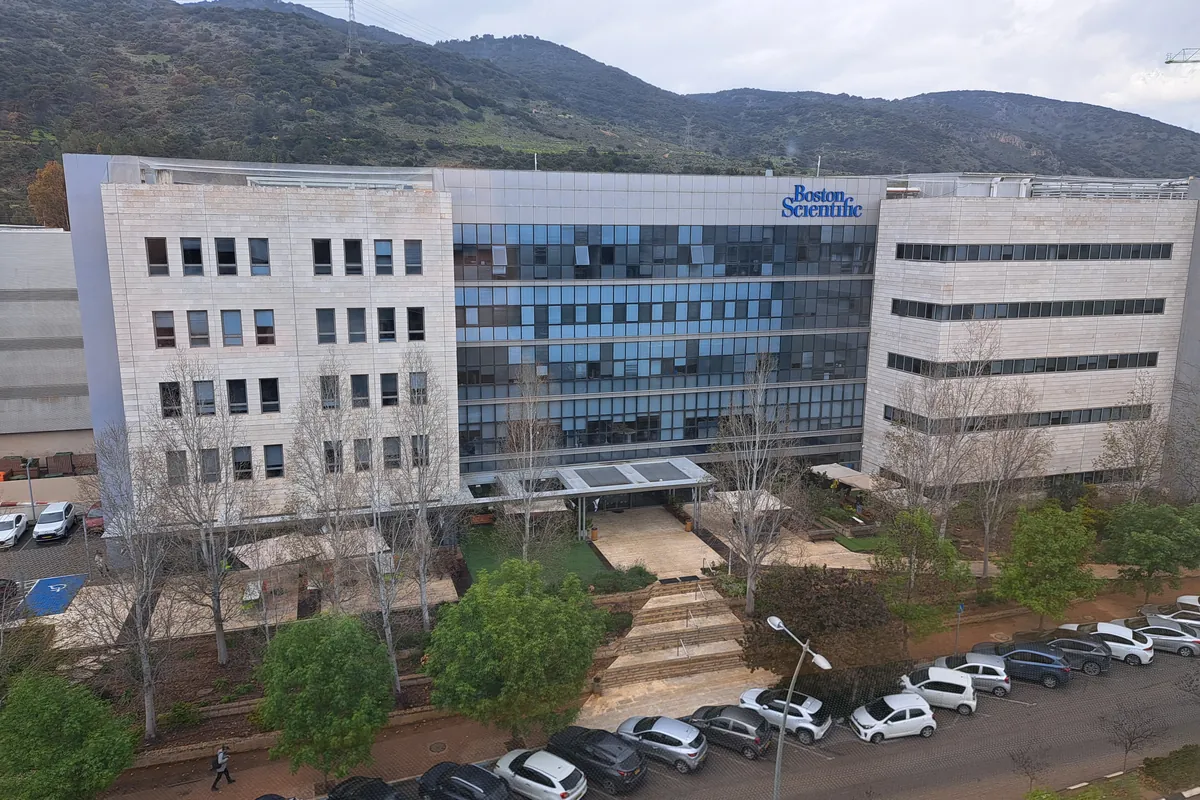
Boston Scientific has told investors that the cyber incident it detected on August 25 is now a financial event. In a Form 8-K filed with the Securities and Exchange Commission on September 8 under Item 1.05, the section reserved for material cybersecurity incidents, the Massachusetts medical device maker said the attack is likely to have a material impact on its results for the third quarter and the full year 2026. As a consequence, it believes it is unlikely to meet the net sales growth and adjusted earnings per share ranges it gave on July 29. A revised outlook will come with third quarter results on October 28.
The filing matters beyond one company. It is one of the clearest cases yet of a large-cap industrial business converting an IT outage into a guidance warning within two weeks, under a disclosure regime that is only in its third year. For investors, it reframes cybersecurity from a cost line into a variable that can move earnings, and for security vendors it is a reminder of what their large customers now stand to lose.
From "not yet determined" to "material"
The sequence of filings is instructive. On August 26 the company filed an 8-K under Item 8.01, the catch-all for other events. It said it had identified an incident affecting certain information technology systems that caused a global disruption to operations, including its ability to process and ship customer orders, and that it had not yet determined whether the incident was reasonably likely to have a material impact.
The September filing goes much further. It describes unauthorized activity that caused a network outage affecting access to operating systems and business applications, and it confirms that the outage hit manufacturing as well as order processing and shipping. Recovery is under way: major distribution centres are shipping at or above normal operating levels, sterilisation facilities are working and manufacturing has resumed across most sites. But the company says the timeline for full recovery is uncertain, and that while it expects to recover some portion of the affected revenue as it works through backlogs, the full impact is not yet known. It does not expect a material effect on its long-term financial condition, and it has found no evidence of ongoing unauthorised access.
That two-step path is exactly what the SEC's staff asked for. Under rules adopted in July 2023, an Item 1.05 report is due within four business days of a company determining that an incident is material. In a May 2024 statement, Erik Gerding, then director of the Division of Corporation Finance, said incidents not yet judged material should be disclosed under another item such as 8.01, keeping Item 1.05 for cases where materiality has been determined. Boston Scientific followed that playbook to the letter.
What the guidance was, and what it now faces
The numbers at risk are specific. On July 29 the company guided to full year net sales growth of about 5.5 to 6.5 percent on a reported basis and adjusted EPS of $3.28 to $3.32. For the third quarter it expected net sales growth of 3 to 5 percent and adjusted EPS of $0.80 to $0.82. Those figures were already reduced: MedTech Dive notes that the company had cut its 2026 forecast twice before the attack, with weaker demand for its Watchman heart implant a recurring theme.
The market reaction on September 8 was modest relative to the words "material impact". Reuters reported the shares down 2.3 percent in morning trading, while MedTech Dive recorded a fall of more than 4 percent to $45.73. According to Quartz, the stock had already lost roughly half its value this year, which may explain why investors treated the filing as confirmation rather than shock. Stifel analysts said investors probably see 2026 as something of a lost year for the company.
Consumables do not wait
The more important analytical point concerns the kind of revenue that was lost. J.P. Morgan analysts drew a contrast with Stryker, which suffered a similar attack in March. Stryker's missed sales were weighted towards capital equipment, which hospitals still need to buy later. Boston Scientific sells mostly single-use devices consumed in procedures, so a procedure that does not happen, or uses a competitor's product, is largely revenue gone for good. Stryker also had nine to ten months to make up the gap; Boston Scientific has about four. J.P. Morgan's Robbie Marcus added, according to Reuters, that the incident clouds visibility into underlying trends in electrophysiology and Watchman, the very franchises investors were already worried about.
That loss of signal is an underappreciated cost. Third quarter numbers will now mix a cyber effect, a backlog recovery and organic demand, and the company will need to separate them convincingly on October 28 if it wants its guidance to be believed again.
What has not been disclosed
The filings are silent on the mechanics. As The Register noted, Boston Scientific has not said how the attackers got in, whether ransomware was involved, who was responsible or whether data was taken, and no group had publicly claimed the attack. Item 1.05 requires a description of the nature, scope and timing of an incident and its likely material impact, not technical detail, and companies have used that latitude. Reuters reported that, in a weekend update, the company said product quality analyses found no impairment beyond disruptions to new activations of its remote monitoring platform for cardiac devices, which The Register described as resolved. For a device maker, that statement on patient-facing systems is arguably the most important disclosure of all.
Reuters also listed Abbott, Stryker, Medtronic and Novo Nordisk among healthcare companies recently hit by cyberattacks. The pattern suggests that highly integrated global manufacturing and logistics, run on shared enterprise systems, has become an attractive target precisely because downtime is so costly.
Implications for investors and security vendors
For equity investors, operational resilience is moving from a governance footnote to a modelled risk. The relevant questions are no longer only whether a company has been breached, but how quickly it can restore manufacturing, sterilisation and order handling, and how much of the lost revenue is recoverable. A business built on consumables and tight hospital inventories has less room than one selling equipment on long cycles.
For security vendors, the Boston Scientific case strengthens the commercial argument for recovery, segmentation and incident response capability rather than detection alone. Boards that read this filing will ask what a fortnight of global downtime would do to their own guidance, and budgets tend to follow such questions. Insurers will ask them too.
Our view
Boston Scientific has handled the disclosure correctly: a prompt holding statement, then an Item 1.05 filing once materiality was clear, with a firm date for numbers. That discipline deserves credit, and it gives other issuers a template. But the episode also shows the limits of the regime. Investors now know the damage is material without knowing its size, its cause or whether data left the building, and they must wait seven weeks to learn more.
The deeper lesson is about business models. Companies whose revenue depends on a continuous flow of consumables cannot store lost sales for later, so their cyber risk is, in effect, an earnings risk. Founders building in medtech supply chains and the security companies that serve them should take note. What to watch on October 28: the size of the revenue hit, how much backlog was recovered, whether the remote monitoring platform is fully restored, and whether management offers any detail on the attack itself.
This article is for information only and is not investment advice.
Sources
- SEC: Boston Scientific Form 8-K, Item 1.05, date of report September 7, 2026
- SEC: Boston Scientific Form 8-K, Item 8.01, filed August 26, 2026
- SEC: Boston Scientific announces results for second quarter 2026
- SEC: SEC adopts rules on cybersecurity risk management, strategy, governance, and incident disclosure
- SEC: Disclosure of cybersecurity incidents determined to be material and other cybersecurity incidents
- MedTech Dive: Boston Scientific unlikely to meet guidance due to cyberattack
- Business Insurance (Reuters): Boston Scientific says unlikely to meet sales forecast after cyberattack
- The Register: Boston Scientific left nursing its bottom line after cyberattack
- Quartz via Yahoo Finance: Boston Scientific misses 2026 guidance after cyberattack
Filed under Cybersecurity. Written by Invest Times Editorial under our editorial standards. Commentary and analysis for information only, not investment advice.